Hiring Agents in 2026
 Operations Center
TL;DR: Agents are becoming commoditized; agent SDKs and vendor solutions make creating them easier. The hard part is operating an office of many agents from many sources, safely connected to company-specific tools. We’re building an Operations Center fronted by an Agent Officer: a registry agent that introduces agents to each other through Slack channels and updates their memories when capabilities change. Tools live with the providers, not the Officer. New agents, including third-party, plug in by registration handshake instead of integration project.
Three months ago I wrote about how we are building an agentic office. Amy on customer support, Navid on servers, Calum on incidents. Agents between people and systems, earning autonomy incrementally.
Since then we’ve added many more. We now have more than 50 agents across customer support, back-office, payments, compliance, security, and other verticals.
The new problem we’re facing is what happens when you have many.
How Amy got complex
Take Amy, our client-support agent, as an example of how this plays out.
Amy was an AI agent. First with static knowledge, then we added tooling. She could answer clients on her own; when she couldn’t, the issue was escalated to a human agent.
At some point we brought Amy into Slack, as per our original agentic office concept.
Then we made her the only client-facing interface. Instead of handing the conversation off, Amy stayed in front and asked humans in Slack for the help she needed. Just enough to answer the client herself.
Then we let her tag other departments directly. Payment, compliance, security. The same handoffs the CS team used to make to other internal teams were now Amy’s job.
Each step made Amy more capable and more complex. She now branches across many decision paths: when to ask CS, when to ask payment, when to involve compliance, what to do with each kind of answer. She’s a small org chart inside one agent.
Then we started bringing in AI agents for the departments Amy was tagging. Atlas for back-office. A payment agent. A compliance agent. A security-requests agent. Each was another colleague Amy could ask instead of pulling in a human.
The office multiplies
These new agents went through their own version of Amy’s path. Each started simple, with one or two capabilities, and grew step by step as we added more functions, giving Amy more she could delegate. Some now handle 20+ kinds of requests.
Every step needs the dev team to integrate the new capability everywhere it’s consumed. Share keys. Update prompts. Wire access. Coordinate across teams. New agents and new capabilities arrive faster than the integrations can follow.
This is the picture that made me start thinking about an operations layer.
What every agent needs
Step back. Every useful agent needs five things:
- SOUL / SKILL: how the agent operates and what it brings. Personality, tone, escalation behavior, what it must never do, the kinds of work it’s capable of.
- Tools: live capabilities. Client status, payment history, KYC, account actions.
- A brain: a model. Increasingly a runtime choice based on quality, cost, latency.
- A Job Description (JD): what the agent is hired to do. Area of expertise, scope of work, who it serves.
- Collaboration: the ability to call other agents and ask humans for help.
Most agents today come with the first three. The fourth is the visionary piece. Don’t confuse JD with SOUL/SKILL: SOUL is how the agent operates, JD is what it’s hired for. An AI engineering manager has SOUL/SKILL (technical review, planning, how it escalates and communicates). But only its JD lets the Operations Center judge that when a developer agent later joins offering coding, this engineering manager would benefit from a channel to it. Without JDs, the office can’t reason about who needs what as it grows. With them, the matching scales without humans in the loop.
The fifth, collaboration, is what the office gives you, and it’s where the integration tax sits.
Operations Center, redrawn
Here’s the architecture.
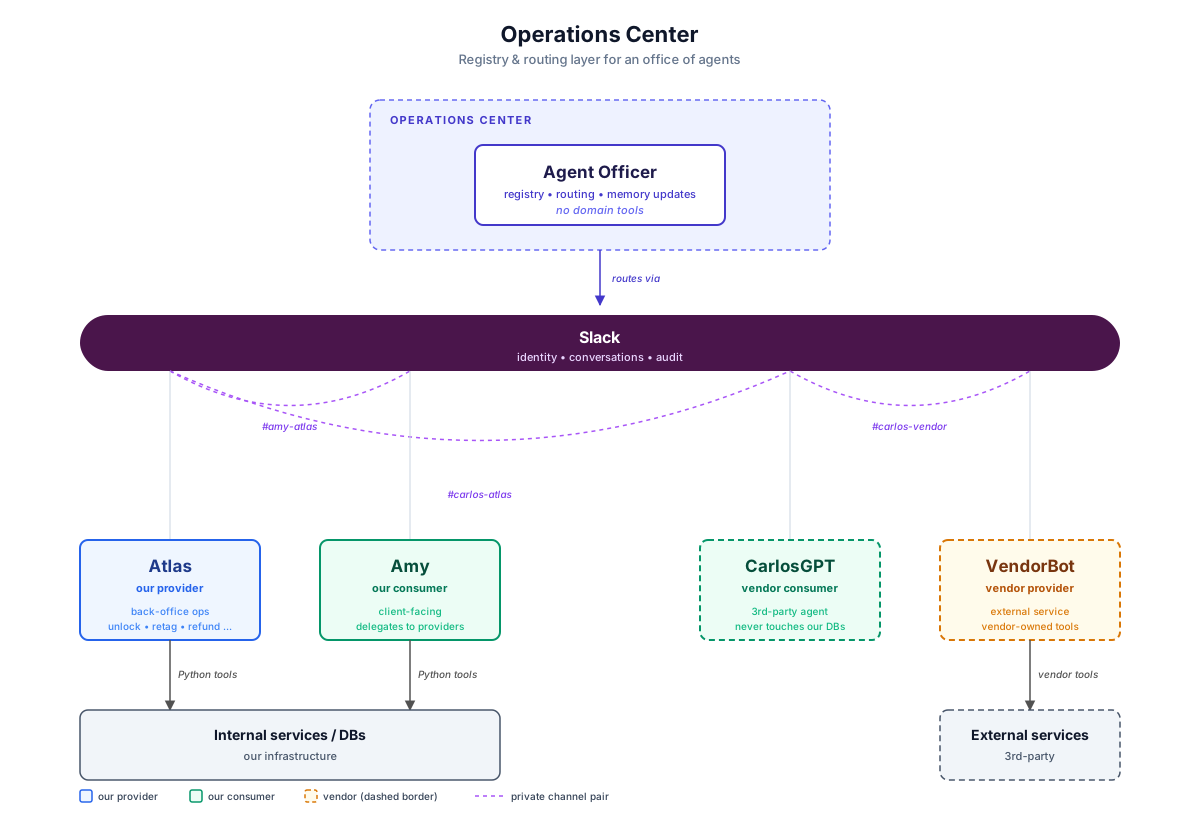 Operations Center architecture
The Operations Center is not a single agent. It’s a collection: a registry of who’s in the office, what each agent provides, what each agent needs, and the operational logic that ties them together.
At the door sits the Agent Officer. It has no business-domain tools. It cannot unlock accounts or inspect payments. Its tools are operational: register an agent, create a Slack channel, update memory, revoke access. What it owns is the operation itself: who’s registered, who provides what, who’s allowed to ask whom, what’s still missing.
The tools and knowledge are distributed across provider agents. Atlas knows back-office data and acts on it. The payment agent owns payment operations. Each provider declares what it offers when it registers. Each consumer declares what it needs.
Once the Officer matches a consumer to a provider, the two talk directly through a private Slack channel. The Officer sets up the introduction and steps back.
Onboarding, step by step
The Officer needs to understand each agent thoroughly to route well. Every registration includes:
- Job description (JD): the full role. Several hundred lines for a serious agent. Who it is, the area of expertise, the work it owns, who it serves. This is the matching key: the Officer reads JDs both at registration and forever after, to judge which other agents’ capabilities would benefit this one.
- What I need: operations the agent expects to consume. Useful as a hint, but the Officer can also infer needs from the JD itself.
- What I provide: operations the agent offers (empty for pure consumers).
Walk through it.
Amy arrives first, as a consumer. She introduces herself with her full job description and a what I need list: unlock user, refund payment, flag KYC, retag affiliate, and dozens more. The Officer registers her and notes which needs are unmet.
Atlas arrives next. Job description, what I need (some things he depends on himself), what I provide, including unlocking user accounts.
The Officer scans the registry. Amy needed unlock user. Atlas provides it. So the Officer:
- Records that Atlas is authorized to answer Amy’s unlock user requests.
- Creates a private Slack channel and invites both agents.
- Updates Amy’s memory: here is Atlas, this is what he provides, this is the channel.
From the next client request that needs an account unlocked, Amy reaches Atlas in the new channel. There was no redeploy and no prompt change. Once Atlas was in Amy’s memory, talking to him in Slack worked as a tool call. For many workflows the Slack conversation itself is enough glue. For regulated or risky actions, the provider still returns structured confirmations and audit records, but the discovery and routing layer is free.
This is, in fact, how Amy works today. The difference is that everything I just described was done by human developers: sharing keys, writing adapters, coordinating across teams. The Officer automates the mundane part of integration.
Updates work the same way
When Atlas gains a new capability later (say, retag affiliate), the same machinery runs.
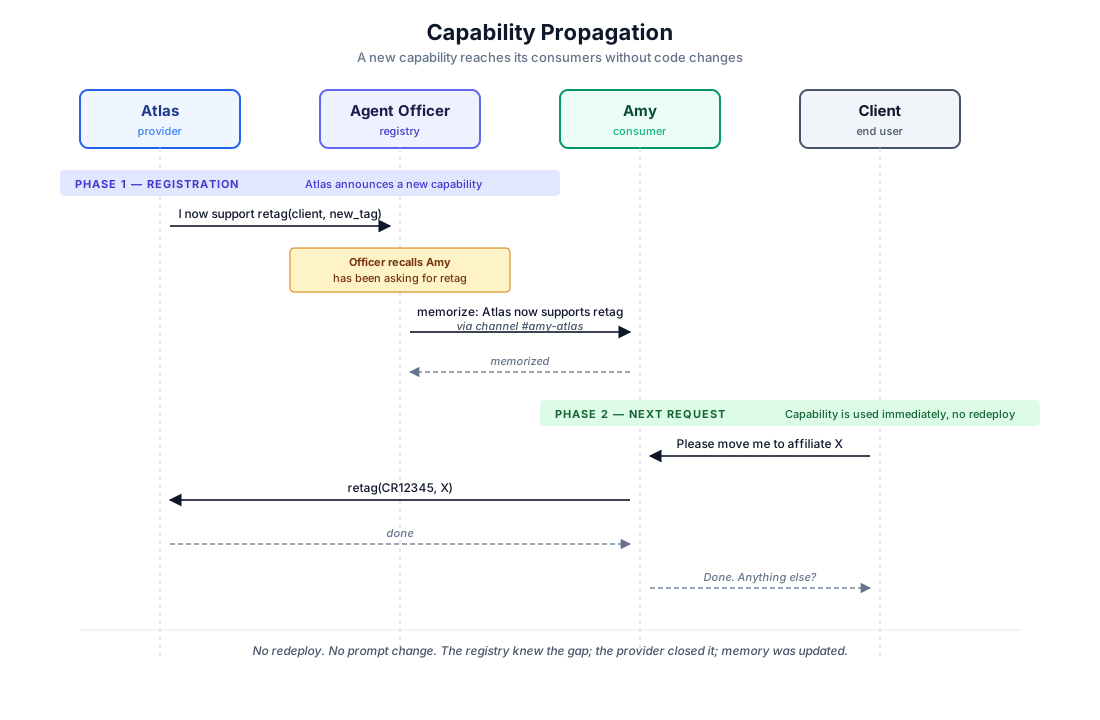 Capability Propagation Sequence
Atlas tells the Officer. The Officer, which kept a record of who needed what, knows Amy was asking for retag. It updates Amy’s memory. The next time a client asks, Amy does it.
The Officer doesn’t only match against explicit need lists. It also reads each agent’s JD and can identify who else might benefit from a new capability, even agents that never listed it as a need. As the office grows, this is what makes the matching scale.
The system gets capable on its own, because the registry knows the gaps and the providers know when they close them.
Memory and permissions
For an agent to join this office cleanly, it needs an updatable operational memory, or at least a managed instruction/config layer the Officer can write to. The Officer has to be able to push updates that persist: “Atlas now supports retag, here’s the channel.”
Whichever surface holds those updates, write authority must be exclusive:
- Registered humans: top authority. Can override anything.
- Agent Officer: one level lower. Updates memory based on registry events.
- Other agents: no write access. They can only converse.
This is the safety brake. An agent’s role, capabilities, and routing live in that surface. If anyone could write there, anyone could redirect the agent. The permissioning is what makes the rest of the architecture trustable.
Bringing in third-party agents safely
A team wants to use OpenAI’s agent product. Another wants Google Workspace. Another wants Claude. Each is genuinely good, fast to set up, well-supported. I want to use them, but I don’t want each one to need a private tunnel into our databases.
In this architecture, they don’t. A third-party agent registers as a consumer through the same handshake (job description, what I need) and gets routed to internal provider agents through Slack channels. The provider agents, which we own and run, sit between the vendor runtime and the data. The vendor’s hosted agent never sees our DBs; it sees Slack messages from another agent.
Adopting a new agent platform becomes a registration handshake, not an integration project.
Trust and access
Once you let agents register and ask each other things, the obvious questions arrive. How do we know CarlosGPT is really CarlosGPT? Who can register it? What can it touch? How do we audit and revoke?
The Officer is the chokepoint for all of them.
- Identity: every agent appears in Slack as a registered account. Slack is the identity layer; messages from any other source are ignored.
- Approval: only a small set of registered humans can introduce a new agent to the Officer. No agent can register another. Human-in-the-loop is the brake on the front door.
- Scope: what an agent is allowed to ask is set at registration. The Officer enforces the routing table; out-of-scope requests go nowhere.
- Audit: every cross-agent channel is a Slack record. Every Officer-issued memory update, registration, and revocation is logged.
- Revocation: a registered human tells the Officer to drop an agent. The Officer leaves the private channels and pushes memory updates to former counterparts.
None of this is bolted on. It falls out of having one registry, one permissioned write surface, one audit trail.
Beyond the office
We’re building a purely AI-driven trading platform. The coding is done by AI (the spec-driven approach I described in Write for the AI That Doesn’t Exist Yet), and the operational management runs on the same Officer pattern as our agentic office.
Every new game ships with a Risk Manager and its own AI bot. Both register with a Game Officer through the same handshake. Just a pattern.
Hiring an agent in 2026
The protocol that emerges is human. You hire an agent the way you hire a person: a manager introduces them in a channel, they’re told who to ask for what, they confirm, they get to work. When something changes, someone walks over and tells them.
We spent years making software talk to software through APIs and schemas. The agentic office runs on a softer protocol, the one humans have used in offices forever. Agents are joining the org chart. The Agent Officer is the chief of staff.
Posted on April 29, 2026